Understand the Risks Behind Everyday Browsing
Why Phishing and Web Threats Remain a Business Risk
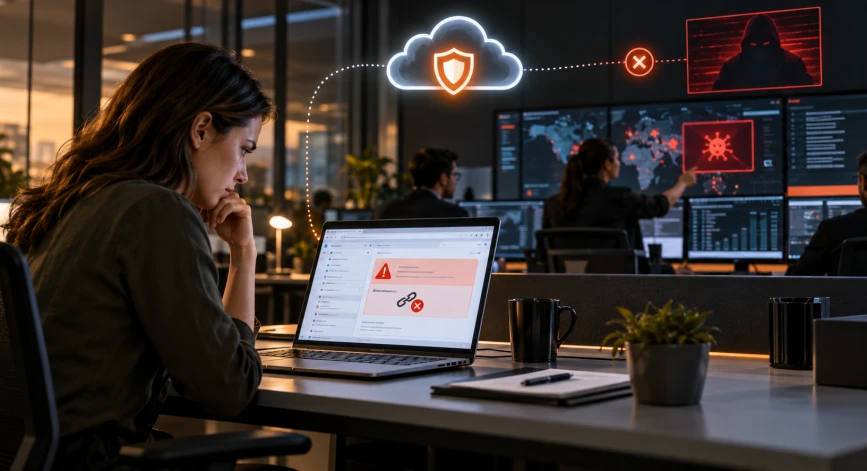
Phishing attacks often succeed by exploiting human behaviour rather than a technical weakness alone. An email may imitate a supplier, a colleague, a bank, or a familiar cloud application. The recipient is encouraged to click a link, open a file, or enter login credentials on a fraudulent website.
Other web threats can emerge when employees visit compromised websites, download infected files, or access online resources that contain malicious content.
For businesses, the consequences can extend beyond an individual device.
Credential theft and account compromise
A convincing fake login page can trick employees into sharing their usernames, passwords, or other authentication details. Attackers may then attempt to access business email, cloud applications, or other accounts.
Malware and ransomware exposure
Malicious websites and downloads can expose users to malware. Depending on the attack and the controls in place, an infected device may become a route for data theft, disruption, or further compromise.
Unauthorized data sharing
Employees may unintentionally upload confidential files to unapproved websites or cloud applications. Without appropriate controls, organizations may have limited visibility into these activities.
Business email and supplier impersonation
Attackers frequently imitate legitimate businesses or trusted contacts to persuade employees to visit fraudulent websites or approve harmful actions. Technical protection can reduce certain risks, but payment verification procedures and employee awareness remain essential.
This is why web security for businesses needs to go beyond blocking a list of known dangerous websites. Organizations need multiple layers of protection that address suspicious destinations, malicious content, risky access patterns, and human error.
Strengthen Your Defence Against Online Attacks
How Zscaler Phishing Protection Works
Zscaler phishing protection relies on security capabilities designed to identify and restrict access to malicious or suspicious destinations. Through services such as Zscaler Internet Access, organizations can apply web security policies to supported internet traffic.
The exact protections available depend on the subscribed services, enabled features, configuration, and traffic being inspected.
Identifying potentially malicious websites
Security systems can evaluate website reputation, URL characteristics, threat intelligence, and other available signals to help identify dangerous destinations. When a website is recognized as malicious or matches a configured security policy, access can be blocked.
This can help reduce the likelihood that employees reach known phishing pages while carrying out routine work.
Applying security policies to internet traffic
Zscaler Internet Access can inspect supported traffic and enforce policies based on the organization’s security requirements. Depending on the configuration, these controls can restrict access to unsafe websites or apply additional security checks.
The aim is to apply security controls consistently instead of relying entirely on employees to recognize every suspicious link.
Helping prevent access to credential-harvesting pages
Credential-harvesting websites are designed to collect login details by impersonating legitimate services. Web security controls can help block access to identified malicious destinations, reducing one route through which credentials may be stolen.
However, no web security product can guarantee that every phishing page will be identified before an attack occurs. Multi-factor authentication, phishing-resistant authentication where appropriate, and employee awareness remain important.
Supporting security monitoring
Security logs and reports, where available and properly configured, can help IT teams investigate blocked destinations, review policy decisions, and identify recurring risks.
This information can inform future policy changes and employee education.
An important distinction: Zscaler helps protect against identified and detectable threats, but phishing protection is not a guarantee against every attack. Newly created websites, compromised legitimate sites, and sophisticated social engineering can still present risks.
Block Risky Websites Before They Cause Harm
How Zscaler URL Filtering Helps Prevent Web Threats
URL filtering is an important part of many enterprise web security strategies. It helps organizations control which websites employees can access based on configured rules, categories, reputation, or other supported security criteria.
Zscaler URL filtering capabilities can help businesses restrict access to known malicious destinations and websites that fall outside organizational policies.
Blocking known malicious URLs
A malicious URL may direct users to a phishing page, malware download, fraudulent login screen, or another harmful destination.
URL filtering can help prevent access when the destination is identified by available security intelligence or matches an applicable policy. This reduces exposure to known threats, although it cannot guarantee detection of every new or modified malicious URL.
Controlling access to risky website categories
Organizations may choose to restrict categories of websites that present unacceptable security or business risks. The appropriate categories and restrictions depend on company policy, employee responsibilities, and business requirements.
A well-designed policy should protect employees without unnecessarily blocking websites needed for legitimate work.
Reducing exposure to suspicious destinations
Security controls may use reputation and threat intelligence to assess website destinations. These signals can help organizations restrict access to sites associated with malicious activity.
Security teams should periodically review policy effectiveness and investigate false positives that affect legitimate business operations.
Applying consistent browsing policies
A centrally managed approach can help organizations maintain consistent web access rules across supported users and locations. This is particularly useful for businesses with branch offices or remote employees.
URL filtering should be combined with other controls, including endpoint protection, identity security, and appropriate monitoring, rather than treated as a complete security solution on its own.
Explore Cloud Threat Prevention for Your Business
Zscaler Malware Protection and Cloud Threat Prevention
Malware can reach business systems through infected downloads, compromised websites, malicious scripts, and other attack paths. Some threats are easy to recognize, while others use changing infrastructure or techniques designed to avoid detection.
Zscaler offers web security and threat prevention capabilities intended to help identify and block malicious activity in supported traffic. These capabilities can form part of a broader cloud threat prevention strategy.
Detecting malicious web activity
Security inspection can help identify certain threats associated with websites, downloads, and supported network traffic. The protection available depends on the enabled security services and the type of traffic being inspected.
Analysing suspicious content
Depending on the licensed features and configuration, organizations may be able to use additional threat analysis or sandboxing capabilities to examine suspicious files or activity.
These capabilities can help identify threats that are not adequately addressed by basic website blocking alone.
Reducing access to harmful downloads
Web security policies can help restrict access to known malicious destinations and downloads. This adds a layer of protection against certain malware delivery methods.
Endpoint detection and response, operating system updates, application patching, and least-privilege access remain important because threats may enter through channels that web security does not cover.
Supporting a layered security strategy
Effective cloud threat prevention combines different controls rather than relying on one product.
A business security strategy should consider:
- Secure web gateway and web filtering controls.
- Endpoint protection and timely software updates.
- Multi-factor authentication and identity security.
- Email security and attachment inspection.
- Employee awareness and phishing reporting.
- Incident response procedures and security monitoring.
The objective is to make successful attacks more difficult and reduce the potential impact if one control fails.
Explore Zscaler Web Security Solutions
FlyingStars can discuss your organization’s internet security requirements and help you explore relevant Zscaler capabilities within its authorized service scope
Apply Stronger Security Across Remote Teams
Zscaler Internet Security Features for Remote Employees
Remote and hybrid working arrangements create additional security considerations. Employees may use home networks, travel between locations, and access cloud applications without passing through a traditional office network.
A cloud-delivered security model can help organizations apply consistent policies to supported internet traffic from different locations.
Secure internet access beyond the office
Zscaler Internet Access is designed to protect internet and SaaS access through cloud-delivered security controls. With an appropriate deployment, organizations can apply policies to supported users who work outside corporate offices.
Help manage web access across distributed teams
Businesses can define acceptable-use policies and restrict access to selected websites or categories. This helps organizations establish consistent expectations across supported users and locations.
Improve visibility into web security events
Available reporting and logging features can help IT teams review blocked traffic, investigate suspicious activity, and identify patterns that may require attention.
The usefulness of these insights depends on configuration, log availability, retention settings, and the organization’s monitoring processes.
Protect access to cloud applications
Employees depend on cloud platforms for communication, collaboration, file storage, and business operations. Appropriate security policies can help reduce exposure to risky destinations and manage selected cloud application activities.
Organizations should also assess identity controls, device security, and data protection requirements to ensure that their overall security strategy covers the relevant risks.
Build a Practical Web Security Strategy
Best Practices for Web Security for Businesses
Technology is only one part of an effective cybersecurity programme. Organizations also need policies, processes, and employee habits that reduce the likelihood of successful attacks.
1. Use layered security controls
Combine web filtering and threat protection with endpoint security, email protection, identity controls, and security monitoring. Different controls address different attack paths.
2. Keep security policies current
Review website categories, access rules, exceptions, and threat protection settings regularly. Business needs change, and policies should be updated accordingly.
3. Strengthen authentication
Use multi-factor authentication for important business accounts and consider phishing-resistant methods for high-risk users and systems. Authentication controls can reduce the impact of stolen passwords.
4. Train employees to recognize phishing
Teach employees to inspect suspicious links, verify unexpected requests, report unusual messages, and confirm sensitive financial or account changes through trusted channels.
5. Patch devices and applications
Keep operating systems, browsers, plugins, and business applications updated. Security patches address known vulnerabilities that attackers may exploit.
6. Monitor and investigate suspicious activity
Review available security logs and alerts, establish escalation procedures, and make sure employees know how to report suspected incidents.
7. Test your controls
Use authorized security assessments and phishing simulations where appropriate. Review the results to identify weaknesses and improve policies, training, and incident response.
A practical security strategy combines appropriate technology with regular reviews and clear responsibilities.
Choose Security Based on Your Business Needs
Is Zscaler the Right Choice for Your Business?
Zscaler may be worth evaluating if your organization wants a cloud-delivered approach to securing internet access, controlling web traffic, and protecting supported users against online threats.
It is particularly relevant to businesses with distributed workforces, extensive SaaS usage, or a need for centrally managed internet security policies.
Before selecting a solution, consider the following questions:
- Which users, devices, and locations need protection?
- What kinds of phishing, malware, and web threats concern your organization?
- Which internet security controls are already in place?
- Do you need URL filtering, advanced threat protection, data protection, or cloud application controls?
- How will the solution integrate with your identity, endpoint, and monitoring systems?
- Which subscription features and implementation services are required?
- Who will manage policies, investigate alerts, and maintain the environment?
A requirements assessment helps determine whether Zscaler Internet Access and its available features match your needs. The right design should address real risks, fit the existing environment, and have a clear operational plan.
FlyingStars is a trusted Zscaler partner and can help businesses explore relevant solutions within the scope of its partnership.
Take the Next Step Toward Stronger Web Security
Explore Zscaler Internet Security with FlyingStars
Phishing and web-based attacks continue to make everyday internet access an important part of enterprise security planning. The right combination of web filtering, threat protection, endpoint security, and employee awareness can help businesses reduce exposure and respond more effectively to suspicious activity.
FlyingStars can help your organization explore relevant Zscaler security capabilities and understand how they may fit into your existing environment.
Looking to improve your business’s phishing and web threat protection?