Understand the Difference Before Choosing
What Is the Difference Between Zscaler and a Traditional Firewall?
A traditional firewall typically controls network traffic according to rules defined for IP addresses, ports, protocols, applications, and other supported attributes. Depending on the product, it may operate as a physical appliance, a virtual appliance, or a cloud-hosted service.
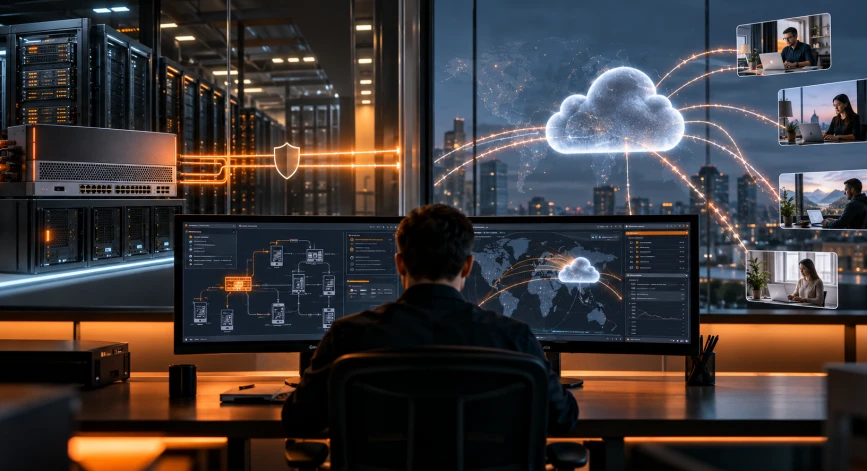
Zscaler is a cloud security platform with multiple services. Zscaler Internet Access (ZIA) focuses on securing access to the public internet and SaaS applications through cloud-delivered security controls. Other Zscaler services address different security requirements, including access to private applications.
The important distinction is that Zscaler is not simply another name for a firewall. ZIA combines several internet security capabilities in a cloud-delivered service, while a traditional firewall is primarily a network traffic control technology. Zscaler also offers cloud firewall capabilities, so the comparison depends on which products and functions are being evaluated.
How a traditional firewall works
A traditional firewall applies traffic rules at a defined network boundary or another configured point in the network. It can allow, restrict, or block traffic based on its rules and available inspection capabilities.
Firewalls remain useful for protecting network segments, controlling inbound and outbound connections, enforcing network policies, and supporting security requirements that depend on specific network boundaries.
How Zscaler Internet Access works
Zscaler Internet Access applies configured security policies to supported internet traffic through the Zscaler cloud platform. Depending on the subscribed features and deployment, it can provide secure web gateway capabilities, URL filtering, threat protection, cloud application controls, and data protection features.
This cloud-delivered approach is designed to support users connecting from different locations without relying exclusively on traffic passing through a central corporate office.
Why the distinction matters
Enterprises need to understand the specific security problem they are trying to solve. Network segmentation, inbound traffic control, remote internet security, SaaS access, and data protection are related but different requirements.
Comparing products by their individual capabilities provides a more useful assessment than assuming one technology can replace every function of another.
Compare the Capabilities That Matter Most
Zscaler vs Traditional Firewall: Key Differences
The following table compares a conventional network firewall deployment with a cloud-delivered ZIA deployment. Actual capabilities vary by firewall vendor, Zscaler subscription, configuration, and network architecture.
| Comparison factor |
Traditional firewall |
Zscaler Internet Access |
| Deployment model |
Commonly deployed as a physical or virtual appliance, though cloud firewall options also exist |
Cloud-delivered internet security service |
| Primary focus |
Network traffic control and protection at configured network boundaries |
Secure access to the internet and SaaS applications |
| Remote users |
May require VPNs or centralized traffic routing, depending on architecture |
Can apply security policies to supported users connecting from different locations |
| Web filtering |
Depends on the firewall’s available web security features |
Includes web security and URL filtering capabilities, depending on configuration |
| Threat protection |
Varies by vendor, subscription, and enabled inspection features |
Offers cloud-delivered threat protection capabilities |
| SaaS security |
Depends on application visibility and available integrations |
Offers cloud application visibility and control capabilities for supported applications |
| Data protection |
Depends on available DLP and inspection features |
Available data protection capabilities depend on licensing and configuration |
| Administration |
May involve separate appliances and management systems |
Provides centralized management for supported Zscaler services |
| Scalability |
May require additional appliance capacity or infrastructure changes |
Designed to scale as cloud service requirements change |
| Internal network protection |
Can protect network boundaries and segments according to its deployment |
ZIA focuses on internet and SaaS access; private application access and internal segmentation require separate architectural consideration |
Which differences should enterprises prioritize?
For a business with many remote employees, consistent internet security and cloud application access may be major considerations. For a data center or internal network, firewall rules, segmentation, and control over specific network connections may remain essential.
A useful comparison should also account for existing licensing, integration effort, traffic routing, business continuity, reporting, and the skills needed to operate each solution.
Find the Best Fit for Your Network
Cloud Firewall vs Zscaler: Are They the Same?
A cloud firewall and Zscaler Internet Access are not necessarily equivalent solutions.
A cloud firewall generally provides firewall functions through a cloud-hosted or cloud-delivered service. Depending on the offering, it may enforce network rules, inspect connections, control application traffic, or protect cloud workloads.
Zscaler Internet Access is a broader internet security service that includes secure web gateway functionality and other available security capabilities. Zscaler also offers cloud firewall functionality within its portfolio, so some features can overlap.
When a cloud firewall may be appropriate
A cloud firewall may be suitable when an organization needs to control network traffic between cloud environments, protect virtual networks, enforce network-level rules, or secure connections between workloads.
The right product depends on whether the main requirement involves cloud infrastructure, internet-bound user traffic, or both.
When Zscaler Internet Access may be appropriate
ZIA may be worth evaluating when the main requirements involve securing user internet access, enforcing web filtering policies, protecting against web-based threats, or managing supported SaaS access across a distributed workforce.
Can an enterprise use both?
Yes. Some organizations may use ZIA for user internet security while retaining firewalls for network segmentation, cloud workloads, data centers, and specialized traffic requirements.
The architecture should define which service inspects each traffic path to avoid unnecessary duplication, routing conflicts, and gaps in protection.
Assess Security Beyond the Network Perimeter
Zscaler Security Comparison: Threat Protection and Access Control
Threat protection is an important part of any Zscaler security comparison, but the results depend on the specific products and features being compared.
Traditional next-generation firewalls may provide intrusion prevention, application control, URL filtering, malware detection, and other advanced security features. Zscaler offers cloud-delivered web and internet security capabilities designed to protect supported traffic.
Neither category should be assumed to provide identical coverage across all threats and deployment scenarios.
Web threats and phishing
Businesses need to reduce exposure to malicious websites, phishing pages, and suspicious downloads. ZIA offers web security and threat protection capabilities. Firewalls may also offer comparable or complementary protection, depending on the product and subscription.
Network-level traffic control
Firewalls are commonly used to control network connections, manage traffic between network segments, and enforce rules based on IP addresses, ports, and protocols.
ZIA’s primary focus is internet and SaaS security. It should not automatically be treated as a replacement for internal network segmentation or every network firewall function.
Application visibility
Organizations need to understand which applications are being used and whether access follows business policy. Zscaler provides cloud application security capabilities for supported services, while firewall application visibility depends on the capabilities and configuration of the chosen product.
Data loss prevention
Protecting sensitive information requires more than blocking malicious websites. Organizations should compare available data classification, inspection, policy enforcement, and reporting features across the products being considered.
For regulated information, validate the relevant controls and coverage against your specific compliance obligations before selecting a solution.
Protect a Distributed Workforce Effectively
Remote Access: Where Zscaler and Firewalls Differ
Remote access is one area where architecture can significantly affect the user experience and the security team’s workload.
Traditional firewall-based designs may route remote employee traffic through a corporate network using VPNs. This can work well, but it may increase dependence on central infrastructure and require additional planning as the workforce grows.
Zscaler Internet Access can apply security policies to supported internet traffic from different locations through its cloud-delivered service.
Remote employees and internet access
Businesses can assess whether cloud-delivered internet security would make it easier to apply consistent browsing and threat protection policies to remote users.
The deployment still requires appropriate traffic forwarding, endpoint configuration, identity integration, and policy management.
Access to private applications
Accessing the public internet is different from accessing an internal application that is not publicly exposed.
ZIA focuses on internet and SaaS access. Organizations considering Zscaler for private application access should separately evaluate Zscaler Private Access (ZPA) and its suitability for their environment.
Performance and user experience
Neither architecture automatically guarantees better performance. Results depend on network routing, user location, application hosting, inspection policies, internet connectivity, and service availability.
Enterprises should test representative workflows and measure performance before rolling out a new architecture across the organization.
Make a Cost Decision Based on Your Actual Needs
Cost Considerations: Zscaler vs Traditional Firewall
Cost comparisons should include more than the initial product price. A firewall deployment may involve hardware, subscriptions, support contracts, upgrades, administration, and infrastructure capacity. A cloud-delivered security service may involve user-based licensing, selected features, deployment work, integrations, and ongoing subscription costs.
Costs associated with traditional firewalls
Depending on the architecture, costs can include:
- Hardware or virtual infrastructure.
- Security subscriptions and vendor support.
- Capacity upgrades and replacement cycles.
- Network engineering and maintenance.
- VPN or remote-access infrastructure.
- Management, monitoring, and incident response.
Costs associated with Zscaler
Depending on the agreement and deployment, costs can include:
- Subscription and user licensing.
- Optional security capabilities.
- Implementation and configuration.
- Identity and network integration.
- Policy administration and operational support.
- Training and ongoing service management.
How to compare total cost of ownership
Use the same evaluation period and include all relevant expenses. Compare the costs of licensing, infrastructure, operations, integration, and any tools that would be retained or retired.
Do not assume that Zscaler is always cheaper or that a traditional firewall always costs less. The answer depends on the existing environment, business requirements, licensing, and operational model.
Build a Security Architecture Around Your Requirements
Enterprise Firewall Alternatives: What Should You Consider?
Businesses exploring enterprise firewall alternatives should begin by defining the requirement behind the search. Replacing a firewall, securing internet traffic, protecting cloud workloads, and enabling private application access are different projects.
Cloud-delivered internet security
For organizations that want to secure user internet access across multiple locations, a cloud-delivered service such as ZIA may be appropriate to evaluate.
Next-generation firewalls
Next-generation firewalls can provide network traffic controls alongside features such as application awareness, intrusion prevention, and threat inspection. The available functionality depends on the vendor and subscription.
Cloud network firewalls
Organizations running applications in public cloud environments may need firewall controls designed for cloud network traffic and workload protection. These requirements should be assessed separately from user web security.
Secure access service edge and zero trust architectures
Businesses modernizing distributed access may consider broader security architectures that combine internet security, access control, and other networking or security functions.
The required components depend on whether the priority is internet access, private applications, network connectivity, or a combination of these needs.
A practical selection checklist
Before choosing an enterprise firewall alternative, review:
- Which traffic and applications need protection?
- Do users work across offices, homes, and branch locations?
- Is network segmentation or cloud workload protection required?
- Which web security and data protection features are essential?
- What integrations are needed with identity, endpoint, and monitoring systems?
- What are the licensing, deployment, and operating costs?
- How will availability, performance, and incident response be measured?
A clear requirements document will make vendor comparisons more useful and help avoid paying for features that do not address the organization’s actual needs.
[Eye Catching Text] Explore Zscaler Solutions for Your Enterprise
How FlyingStars Can Help with Zscaler Evaluation
FlyingStars is a trusted Zscaler partner. Organizations evaluating Zscaler can discuss their requirements with FlyingStars and explore relevant solutions within the scope of the partnership.
A productive evaluation starts with the existing environment rather than assuming a particular product must replace every security control.
Review your current architecture
Identify existing firewalls, remote-access arrangements, internet gateways, cloud services, and security monitoring tools.
Identify gaps and overlapping capabilities
Determine which security controls are working well, where additional protection is needed, and where multiple tools may perform similar functions.
Evaluate relevant Zscaler services
Consider ZIA for internet and SaaS security, and evaluate other products separately if private application access or additional capabilities are required.
Define deployment and support requirements
Clarify licensing, integration, implementation responsibilities, testing, and ongoing operational arrangements before proceeding.
The objective is to help your organization make an informed decision that aligns with its security priorities, technical environment, and budget.
Final Thoughts: Zscaler vs Traditional Firewall
The comparison between Zscaler and traditional firewalls is ultimately about choosing the right security controls for the traffic, users, and applications an organization needs to protect.
Traditional firewalls continue to serve important network security functions. Zscaler Internet Access offers a cloud-delivered approach to internet and SaaS security that may be particularly relevant to distributed workforces and cloud-first businesses.
For many enterprises, the decision does not have to be an either-or choice. A combination of cloud-delivered security and traditional network controls may provide the most suitable architecture.
Before making a decision, assess your existing environment, identify security gaps, compare the relevant capabilities, and calculate the total cost of ownership.
If your organization is considering Zscaler, FlyingStars can help you explore relevant options and determine the next steps based on your requirements.