Start with the Basics of ZIA
What Is Zscaler Internet Access?
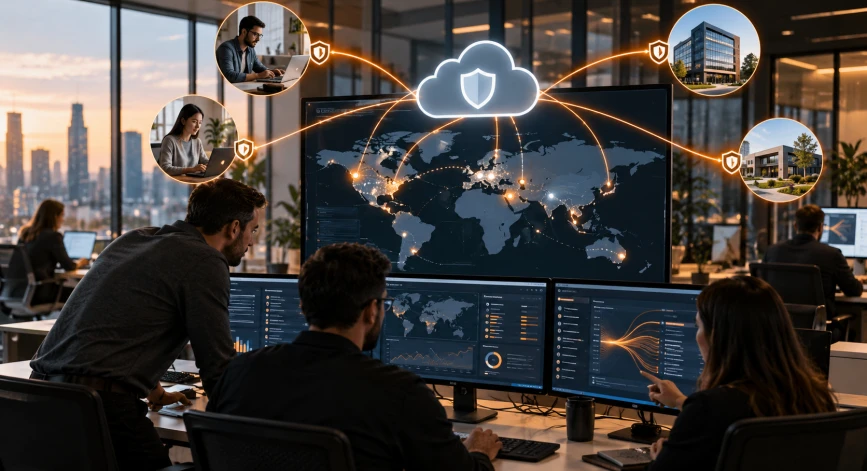
Zscaler Internet Access, commonly called ZIA, is a cloud-native security service that protects users accessing the internet and SaaS applications. It is part of the Zscaler Zero Trust Exchange platform and uses cloud-delivered security controls to help organizations manage internet traffic and reduce exposure to online threats.
In simple terms, ZIA acts as a security inspection point between users and the internet. Instead of allowing traffic to reach its destination without the appropriate checks, the service evaluates it against configured security policies.
For example, if an employee attempts to access a website known to distribute malware, the relevant security policy may block the connection. If the employee accesses a legitimate business application, the service applies the applicable controls and allows traffic according to the organization’s policies.
ZIA can support organizations with office-based employees, remote teams, branch locations, and cloud-first operations.
What does ZIA actually do?
The ZIA security platform brings together several internet security capabilities, depending on the organization’s subscription and configuration.
- Secure Web Gateway: Inspects web traffic and enforces browsing policies.
- URL Filtering: Helps restrict access to malicious or prohibited websites.
- Threat Protection: Helps detect and block certain types of malware, phishing, and other web-based threats.
- Cloud Application Controls: Helps organizations manage the use of supported cloud applications.
- Data Loss Prevention: Supports policies designed to prevent unauthorized exposure of sensitive information.
- Cloud Firewall: Provides firewall capabilities for supported traffic and network services.
These capabilities can work together to help security teams apply consistent controls without managing every security decision through separate office-based appliances.
Who uses Zscaler Internet Access?
ZIA may be useful for organizations that need to protect a distributed workforce, manage internet access across multiple locations, improve web security, or apply consistent policies to cloud application usage.
It is particularly relevant to businesses that are reviewing traditional internet security infrastructure and considering a cloud-delivered alternative.
Follow a Web Request Through ZIA
How Does Zscaler Work?
Understanding how Zscaler works becomes easier when you follow a typical employee’s internet request.
Suppose an employee working from home needs to open a cloud-based business application. Depending on the deployment, the employee’s supported traffic is forwarded to the Zscaler service using an appropriate traffic-forwarding method.
The service identifies the relevant user or connection context, evaluates the configured policies, inspects supported traffic, and determines whether the request should be allowed, restricted, or blocked.
Step 1: The user connects to the internet
An employee opens a browser or a supported application and requests access to an internet destination. The request may originate from an office, a home network, or another supported location.
Step 2: Traffic is forwarded to the Zscaler service
Depending on the organization’s setup, traffic may be forwarded using Zscaler Client Connector, tunnels, proxy auto-configuration (PAC) files, or other supported forwarding methods.
The forwarding configuration determines which traffic is sent to the service and how users are identified.
Step 3: ZIA evaluates the security policies
The service applies the relevant policies based on available information, such as user identity, location, device context, destination, and traffic type.
For example, a company may allow access to approved business applications while blocking certain categories of websites.
Step 4: Traffic is inspected for threats
Applicable security controls examine supported traffic for indicators of malicious activity and policy violations. Depending on the enabled services, this may involve URL filtering, threat detection, firewall rules, or data protection controls.
Encrypted traffic inspection depends on the organization’s TLS inspection configuration, applicable policies, and any exclusions.
Step 5: The request is allowed or blocked
If the request meets the applicable policies, the service permits the traffic to proceed. If the request violates a blocking policy or is identified as a threat, the service can block it.
Security events and activity records can help administrators investigate incidents and review policy decisions.
Step 6: Administrators review and improve policies
Security teams can use available reporting and logs to understand activity, investigate potential threats, and refine security rules as business requirements change.
The result is a policy-driven approach to internet security that can follow supported users beyond a single corporate network.
Understand the Technology Behind the Service
Understanding ZIA Architecture
ZIA architecture is designed to deliver internet security through a cloud service rather than requiring every user connection to pass through a security appliance at a corporate headquarters.
Its architecture includes traffic-forwarding mechanisms, cloud-based service infrastructure, security policy enforcement, and management capabilities.
Traffic forwarding
Traffic forwarding connects users and locations to the Zscaler service. The appropriate method depends on the environment.
Common approaches include:
- Zscaler Client Connector for supported user devices.
- GRE or IPsec tunnels for supported network environments.
- PAC files for supported proxy-based forwarding.
- Other supported connectors and forwarding options for specific deployment needs.
Organizations may use more than one method to accommodate office networks, remote employees, and different device types.
Cloud-based security inspection
Once traffic reaches the relevant Zscaler service edge, applicable security controls inspect it and enforce configured policies. These controls can include web security, firewall filtering, threat prevention, and data protection, depending on the licensed services.
Identity and policy enforcement
Security rules can be configured around users, groups, departments, locations, and other supported conditions. This allows businesses to create policies that reflect different roles and operational requirements.
For example, a finance team may need different access permissions from a general guest network. Policy design should reflect the organization’s risk assessment and business needs.
Centralized administration and reporting
Administrators manage security policies and review available activity records through the platform’s management capabilities. Reporting can help teams investigate suspicious activity and assess whether existing policies need adjustment.
How ZIA architecture differs from traditional security
Traditional architectures often route internet traffic through centralized data centers or office-based security appliances. ZIA can provide cloud-delivered inspection for supported traffic, reducing dependence on that centralized model.
However, a successful deployment still requires careful planning for traffic forwarding, identity integration, application compatibility, connectivity, and existing security controls.
Explore the Features That Matter Most
Key Zscaler ZIA Features
The main Zscaler ZIA features are designed to help businesses manage internet access, inspect supported traffic, and protect users from online threats. The exact features available depend on the selected subscription and configuration.
Secure Web Gateway
The Secure Web Gateway helps inspect web traffic and enforce browsing policies. It can help prevent access to risky destinations and reduce exposure to web-based threats.
URL Filtering
URL filtering allows organizations to create rules for website categories and destinations. This helps security teams restrict access to known malicious websites and apply acceptable-use policies.
Advanced Threat Protection
Available threat protection capabilities help identify malicious activity, including certain forms of malware, phishing, and suspicious web content.
Cloud Application Security
Cloud application controls can help organizations manage access to supported SaaS applications and apply policies to reduce risks associated with inappropriate usage.
Data Loss Prevention
Available DLP features help identify and control the movement of sensitive information across supported channels. Businesses should check which data types, applications, and traffic paths are covered by their selected services.
Firewall and DNS Security
Firewall controls can enforce rules for supported network traffic. DNS security can help block access to malicious domains and identify certain suspicious DNS activity, depending on the available services.
Security visibility and reporting
Available logs, reports, and integrations help security teams understand policy enforcement and investigate potential incidents.
Connect Security Benefits to Business Needs
What Are the Main Benefits of ZIA?
The value of ZIA depends on how well its capabilities match an organization’s security requirements. For businesses with distributed users and cloud-based applications, its cloud-delivered model can offer several practical advantages.
Consistent security across locations
Organizations can apply common security policies to supported users in offices, homes, and other locations. This helps reduce reliance on the assumption that users are protected simply because they are connected to a corporate network.
Reduced dependence on centralized infrastructure
A cloud-delivered security model can reduce the need to route all internet traffic through a central office or data center. The impact depends on the existing architecture and deployment design.
Better control over internet access
Web filtering and related policies help organizations decide which destinations and applications users can access. These controls can support both security requirements and acceptable-use policies.
Support for threat prevention
Applicable security features can help identify and block certain malicious web activity before it affects users. Effective protection still depends on the enabled features, configuration, and broader security practices.
More centralized policy management
A cloud-delivered platform can help security teams manage selected policies through a common management environment instead of maintaining separate rule sets across many appliances.
Support for cloud-first operations
Organizations that depend heavily on SaaS applications can evaluate ZIA as part of a wider strategy for protecting internet and cloud application access.
ZIA is not a replacement for every cybersecurity control. Endpoint protection, identity security, secure application development, employee awareness, and incident response remain important parts of a complete security strategy.
See How Businesses Can Apply ZIA
Common ZIA Use Cases for Enterprises
ZIA use cases vary by organization, but several business scenarios illustrate where cloud-delivered internet security may be relevant.
1. Securing remote employees
A business with employees working from home may want to apply consistent internet security policies without relying exclusively on office-based infrastructure. ZIA can help protect supported remote-user traffic through the configured security controls.
2. Protecting branch offices
Organizations with multiple branches can evaluate cloud-delivered security as a way to standardize selected internet security policies across locations.
3. Controlling access to websites
Businesses may need to block malicious destinations, restrict inappropriate website categories, or apply different policies to different employee groups. Available URL filtering and web access controls can support these requirements.
4. Managing SaaS application usage
Employees often use cloud applications to share files, communicate, and manage business information. Cloud application controls can help organizations understand usage and enforce applicable policies for supported applications.
5. Reducing web-based security risks
Organizations can use available threat protection capabilities to help identify phishing, malware, and other malicious web activity.
6. Supporting data protection policies
Businesses handling sensitive customer or financial information can evaluate available DLP features to help prevent unauthorized information transfers through supported channels.
7. Modernizing legacy web security
Organizations reviewing older web gateways or internet security appliances can assess whether ZIA could replace selected functions or complement existing controls as part of a phased transition.
Each use case should be assessed against actual requirements, existing technology, licensing, and implementation effort.
Choose the Right Security Model for Your Organization
Zscaler ZIA vs Traditional Internet Security
ZIA and traditional internet security architectures can both play a role in protecting enterprise traffic, but their approaches to delivering security differ.
| Area |
Traditional internet security |
Zscaler Internet Access |
| Delivery model |
Often depends on physical or virtual appliances |
Cloud-delivered security service |
| Remote users |
May rely on VPNs or centralized traffic routing |
Can protect supported users across locations |
| Traffic inspection |
Depends on appliance placement and capacity |
Inspection through the Zscaler cloud service |
| Policy administration |
May involve multiple devices and management consoles |
Centralized management for supported security policies |
| Scalability |
May require appliance upgrades or added infrastructure |
Designed to scale through cloud-delivered infrastructure |
| Deployment considerations |
Hardware, routing, capacity, and maintenance |
Licensing, traffic forwarding, identity, policies, and integrations |
The comparison depends on the specific products and architecture being evaluated. ZIA does not automatically replace every network firewall or private application access solution. Businesses should assess their full requirements before deciding which controls can be consolidated or replaced.
Take the Next Step Toward Better Web Security
Explore Zscaler Internet Access with FlyingStars
Understanding ZIA is a useful starting point, but choosing the right security approach requires a closer look at your organization’s users, applications, existing infrastructure, and risk exposure.
FlyingStars is a trusted Zscaler partner and can help businesses explore relevant Zscaler solutions within the scope of its partnership. Discuss your current security environment and determine which options may be suitable for your requirements.
Want to explore Zscaler Internet Access for your organization?